
GitLab
Inline MR review + on-demand runs
Connect gitlab.com or your own GitLab with an OAuth application or a personal access token, and let ArchPilot comment on merge requests. You can also trigger a review on a specific MR from the panel - the scan runs in your own GitLab CI.
Auth: OAuth application or personal access token

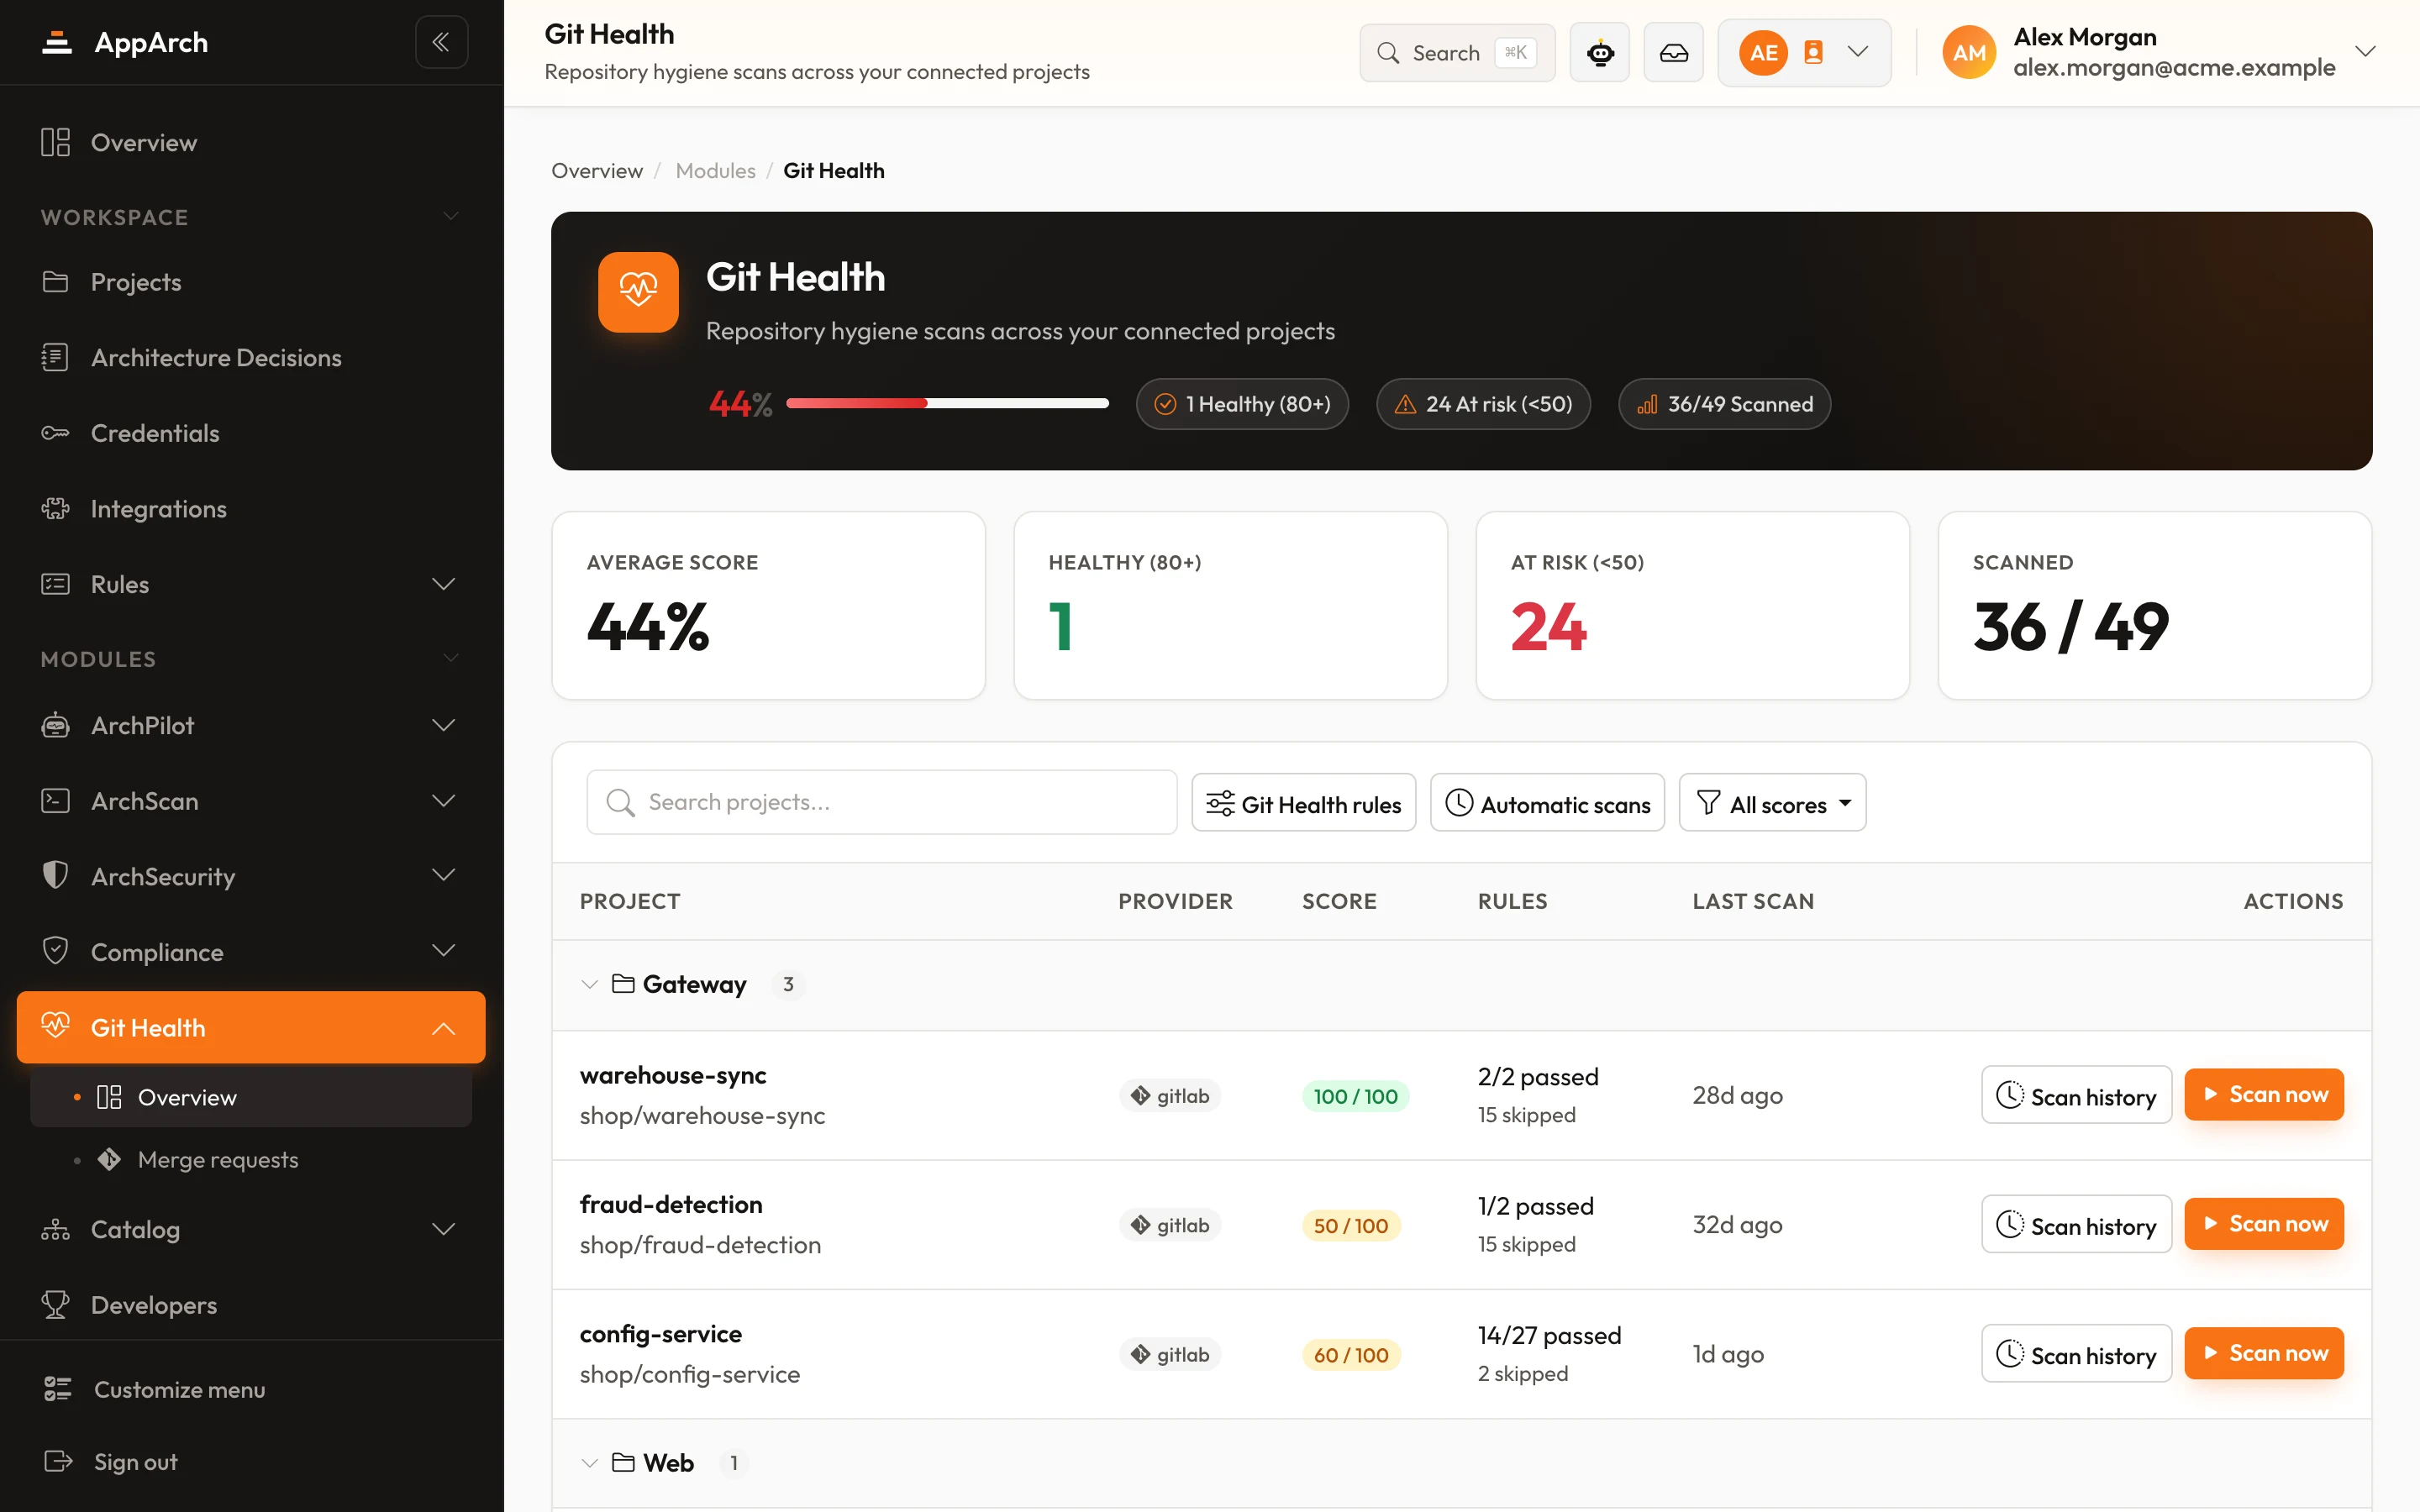
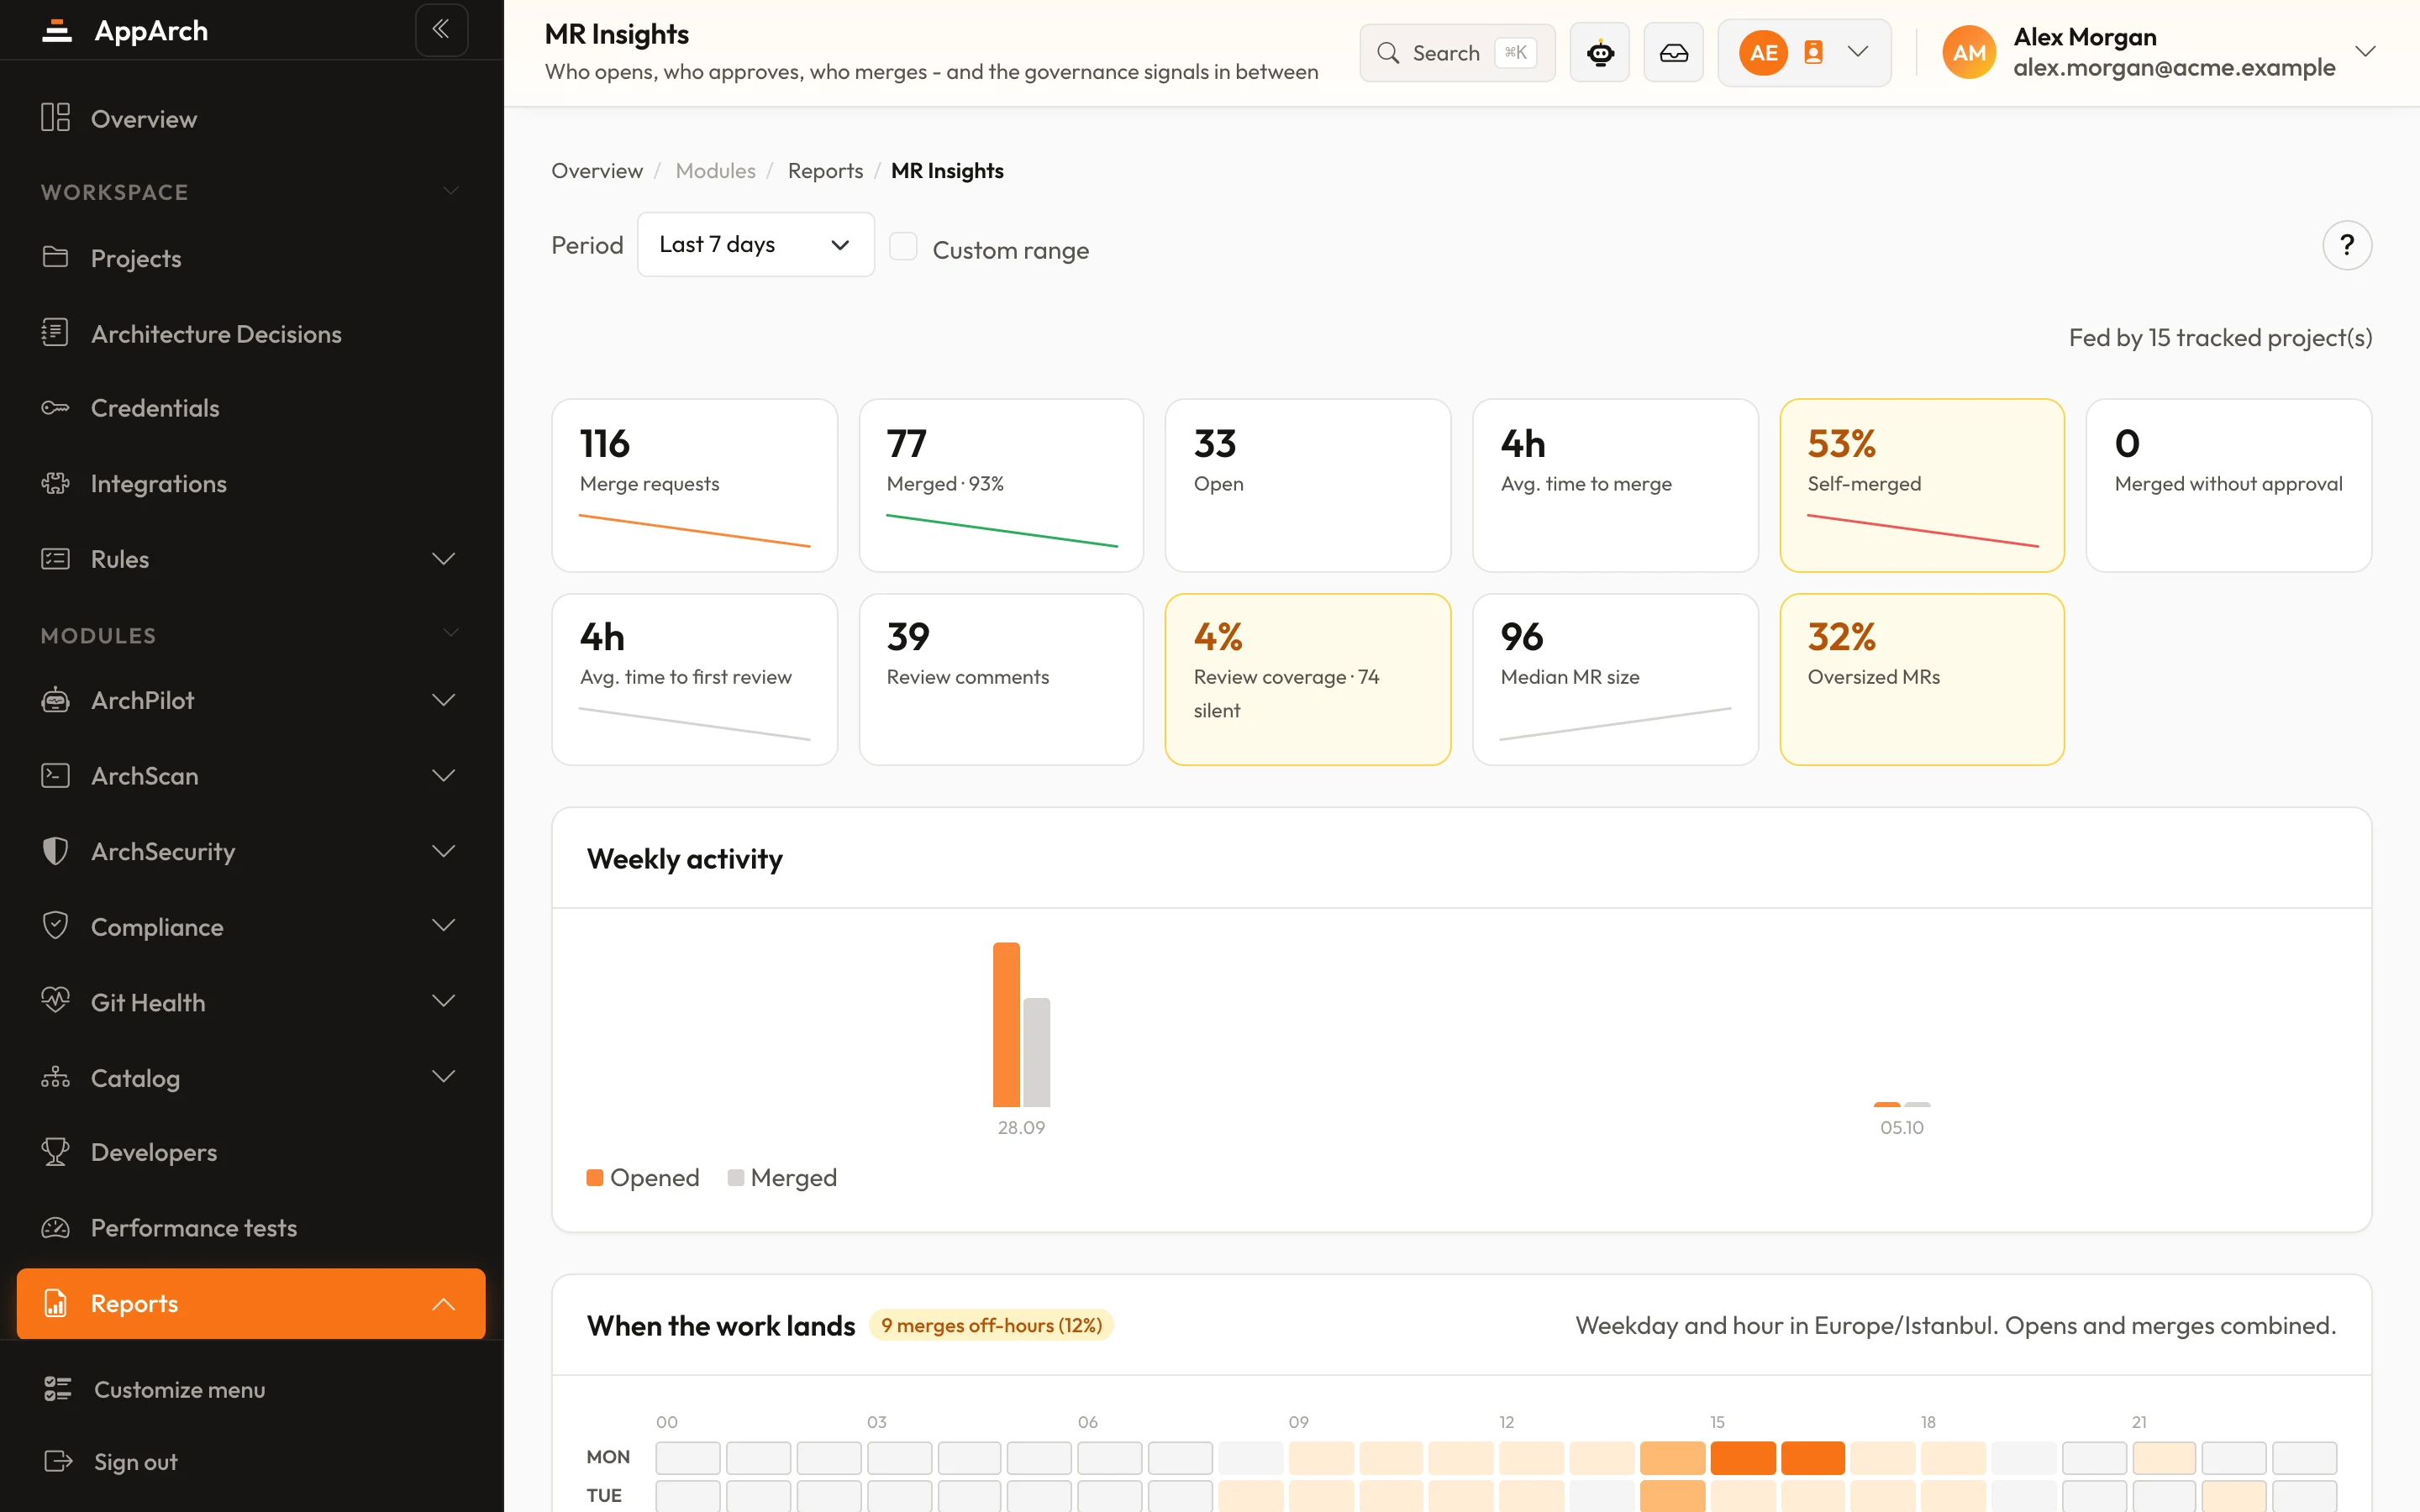
Screens from a running installation
How it connects
- 01
Connect
Register an OAuth application or paste a personal access token; a self-hosted instance takes its own URL.
- 02
Pick projects
Choose the GitLab projects to review.
- 03
Open or trigger an MR
Review automatically, or kick one off from the panel.
What you get
Inline MR comments
Architecture feedback scoped to the diff.
On-demand manual review
Scan a specific MR from the panel in one click.
Runs in GitLab CI
Analysis runs in your pipeline and never leaves your infrastructure.
Comment language
Pick the language ArchPilot writes in, per workspace.
How it works inside AppArch
Your AppArch server talks to the Git platform; the analysis runs in your CI. Here is every call in both directions.
What it reads
- Repositories, branches and members; members every 10 minutes for Developer Sync
- Merge requests, approvals and review threads; MR facts every 15 minutes for MR Insights
- Branch protection and merge settings, for Git Health
- Single files and the file tree, for Compliance; nothing is cloned
- The vulnerability report every 4 hours (GitLab Ultimate), into ArchSecurity
What it writes
- Inline comments on the lines the change added
- An AppArch section in the MR description, or one summary comment if that edit fails
- Resolves its own thread once the finding is gone
- Optional auto-approve or auto-reject; it refuses to approve if new commits arrived after the review
- Starts merge request and branch pipelines for on-demand runs, and can write CI variables
- Auto-reject withdraws the approval and leaves a note, since GitLab has no rejection
What it never does
- No commit statuses or check runs: the pipeline result is your CI job's own exit code
- Never clones or uploads the repository to the panel
- Never registers webhooks itself; paste the URL if you want one
An OAuth application (api, read_user, read_repository) or a personal access token with api. OAuth tokens are refreshed two minutes before they expire. gitlab.com or your own instance by URL.
When things happen
- 5 sComments are posted
- 10 sNew findings are matched to their threads
- 5 minMerge request state and approvals are re-read
- 10 minMembers are synced
- 15 minMR facts for MR Insights
A webhook makes the merge request state change immediate instead of waiting for the next poll.
See it in the product
All screenshots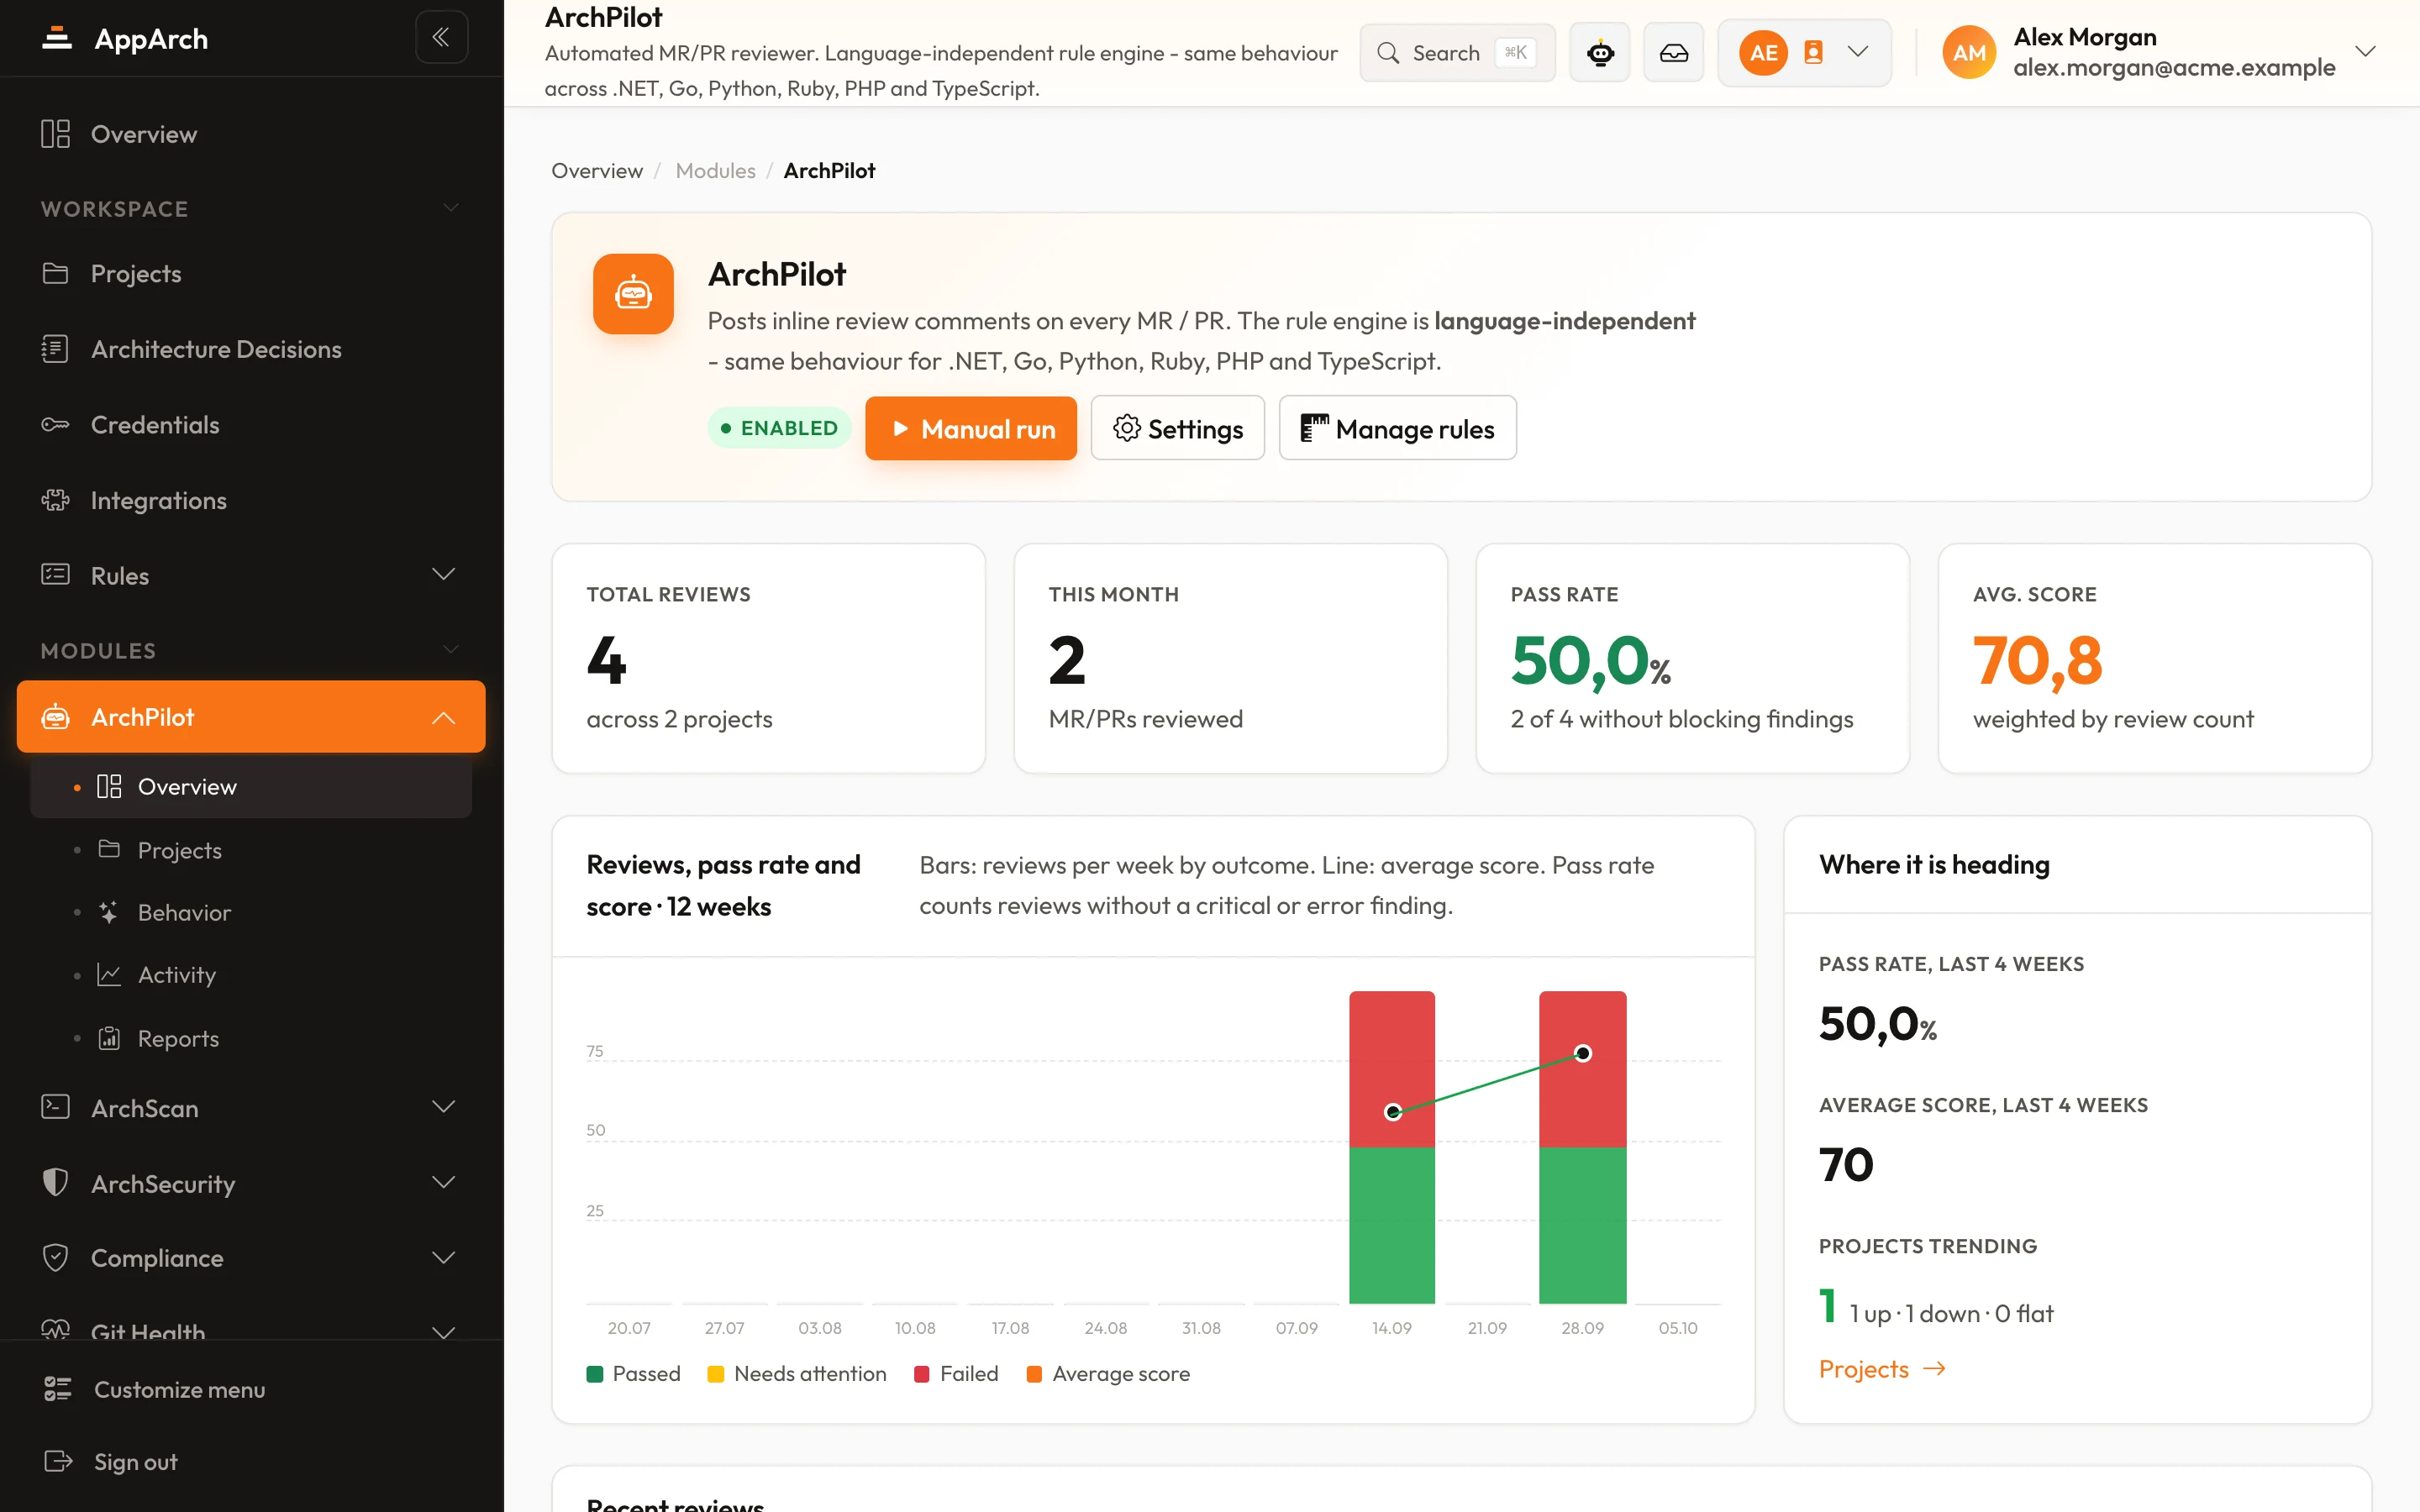
Connect GitLab
Connect in minutes - your first review lands on the next change.