
GitHub
Automated architecture review on PRs
Connect GitHub with a personal access token, fine-grained or classic. ArchPilot leaves inline comments on every pull request, while ArchScan and ArchSecurity reports flow to your panel.
Auth: Personal access token (fine-grained or classic)

Screens from a running installation
How it connects
- 01
Create a token
A fine-grained or classic token with access to the repositories you want reviewed. Its expiry date is shown in the panel.
- 02
Select repositories
You choose which repositories are reviewed.
- 03
Open a PR
ArchPilot reads the diff and comments on the relevant line.
What you get
Inline PR comments
Finding, rationale and suggested fix, right on the line.
Runs in your CI
Analysis runs in your GitHub Actions; the code never leaves.
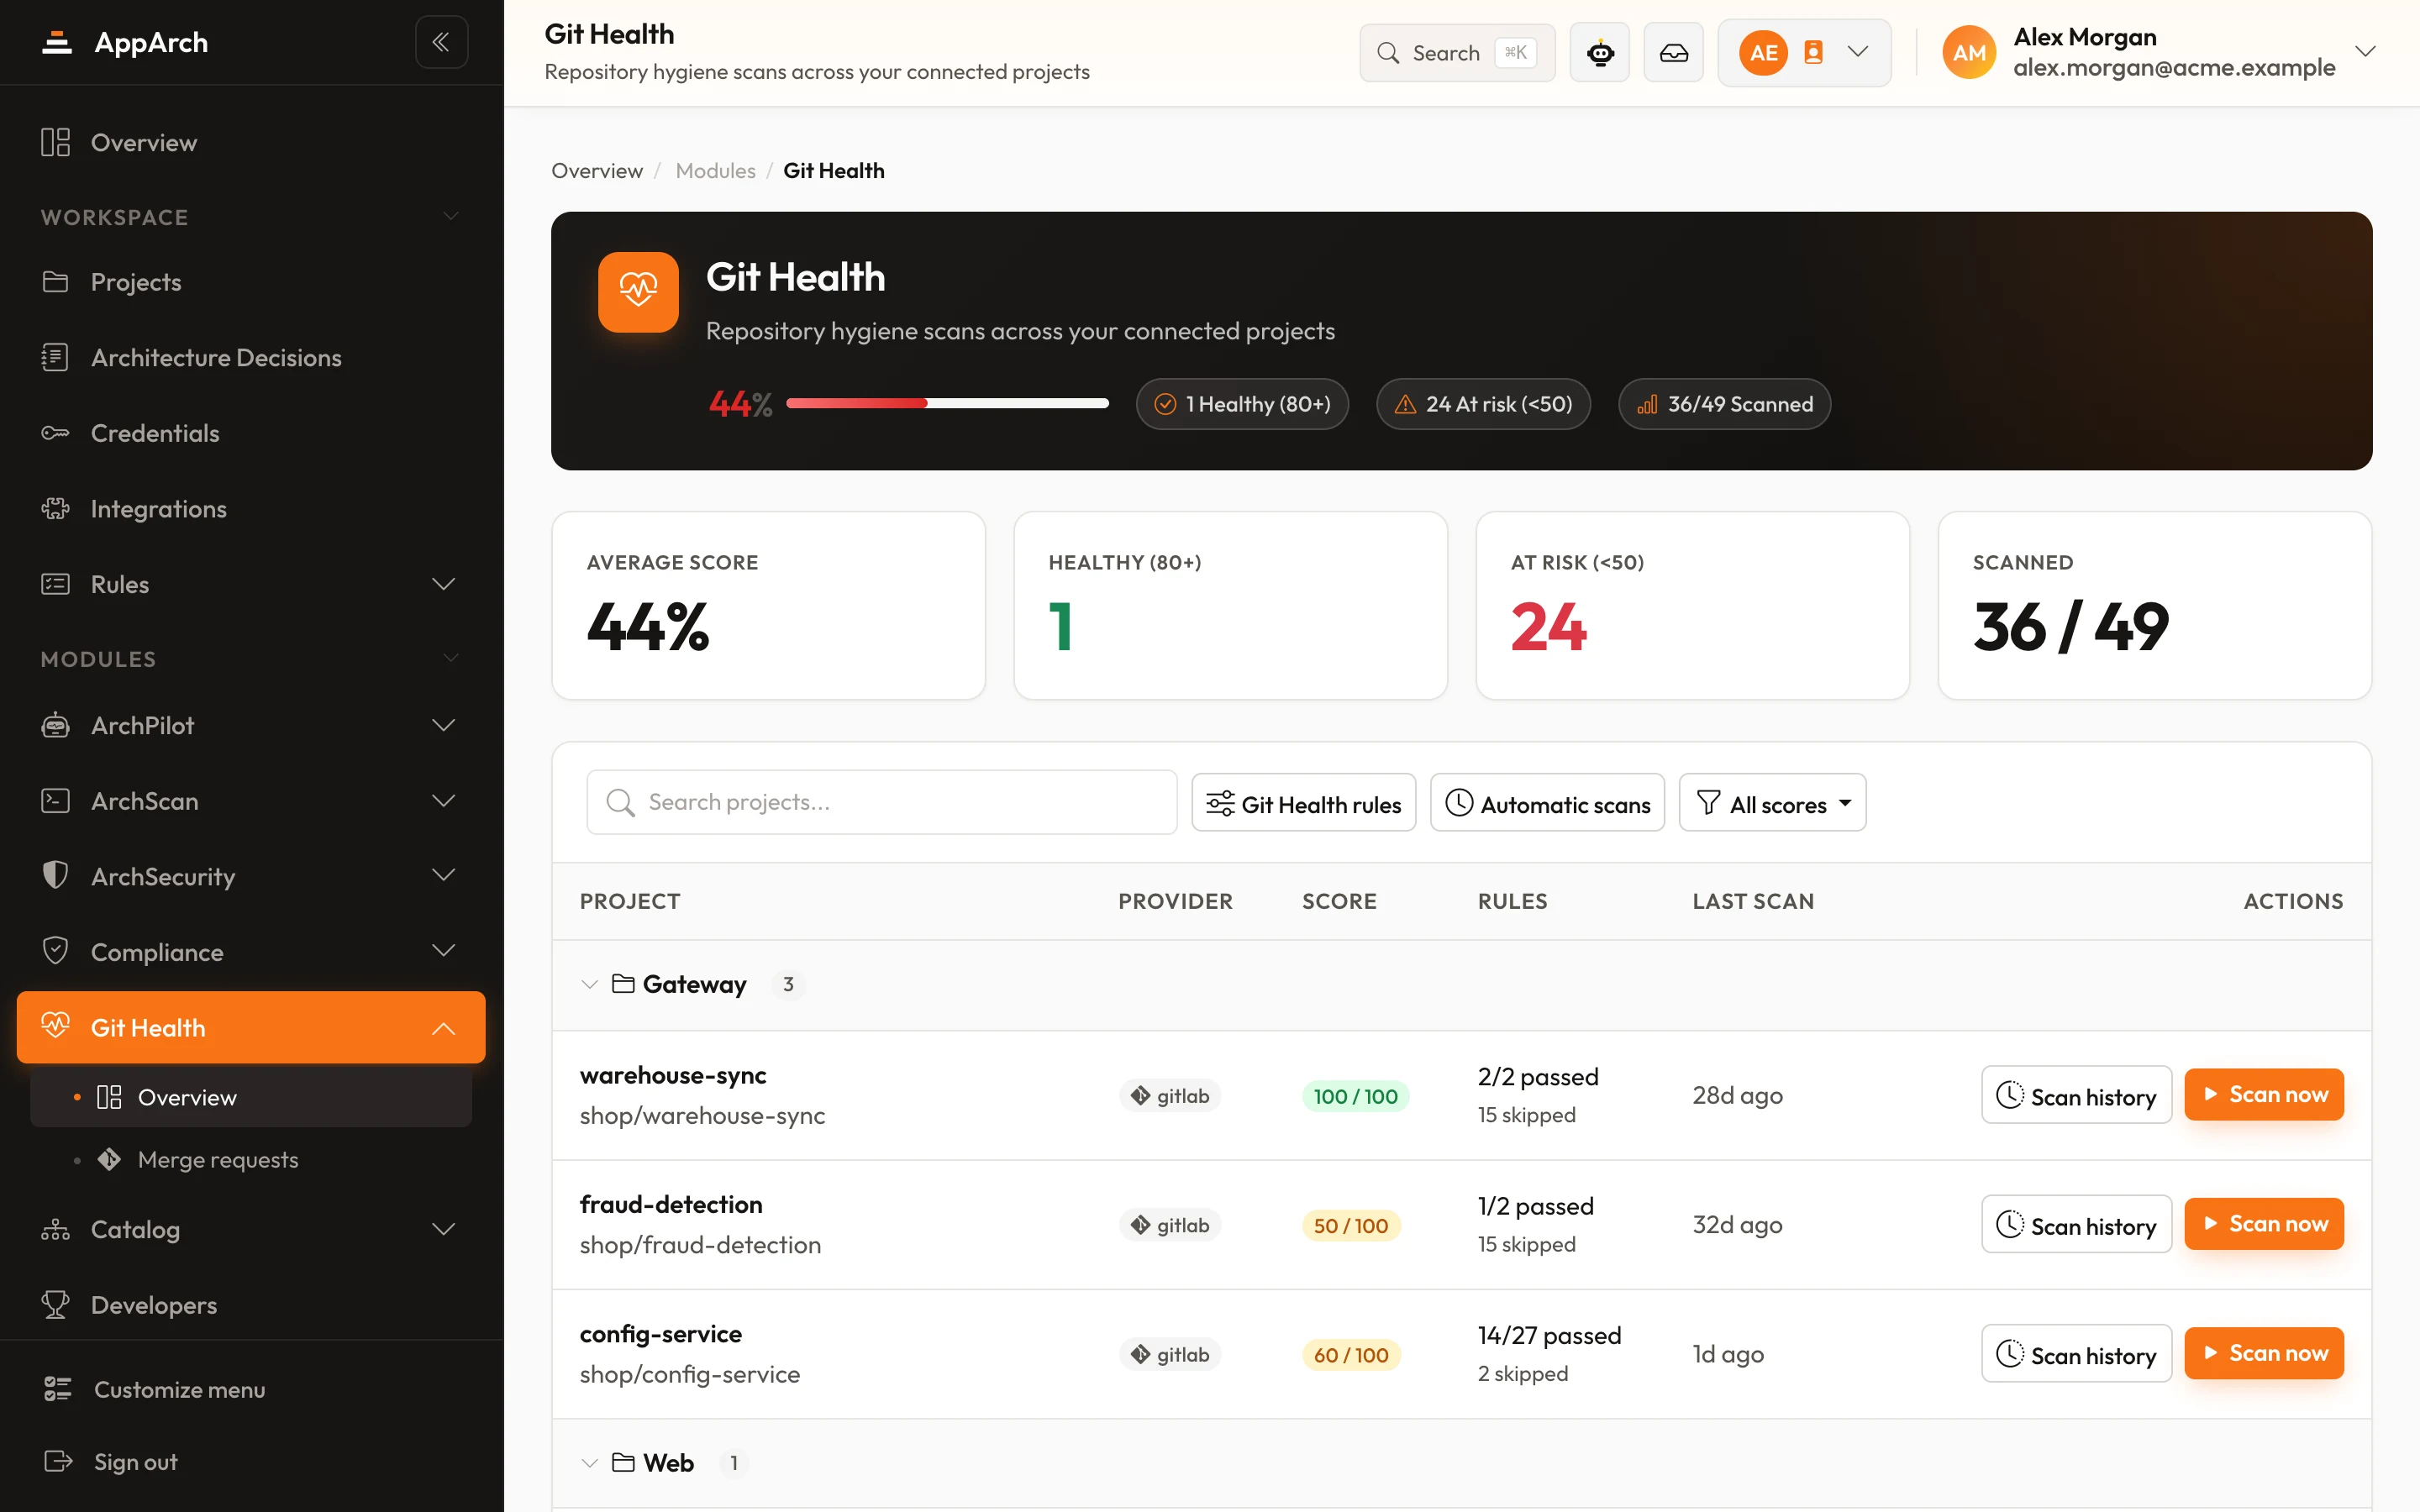
Git Health on GitHub
Branch protection, review rules and security tooling in Actions, scored per repository.
Token renewal in place
When a token nears its expiry, the operator replaces it on the same connection; nothing has to be set up again.
How it works inside AppArch
Your AppArch server talks to the Git platform; the analysis runs in your CI. Here is every call in both directions.
What it reads
- Repositories, branches and members; members every 10 minutes for Developer Sync
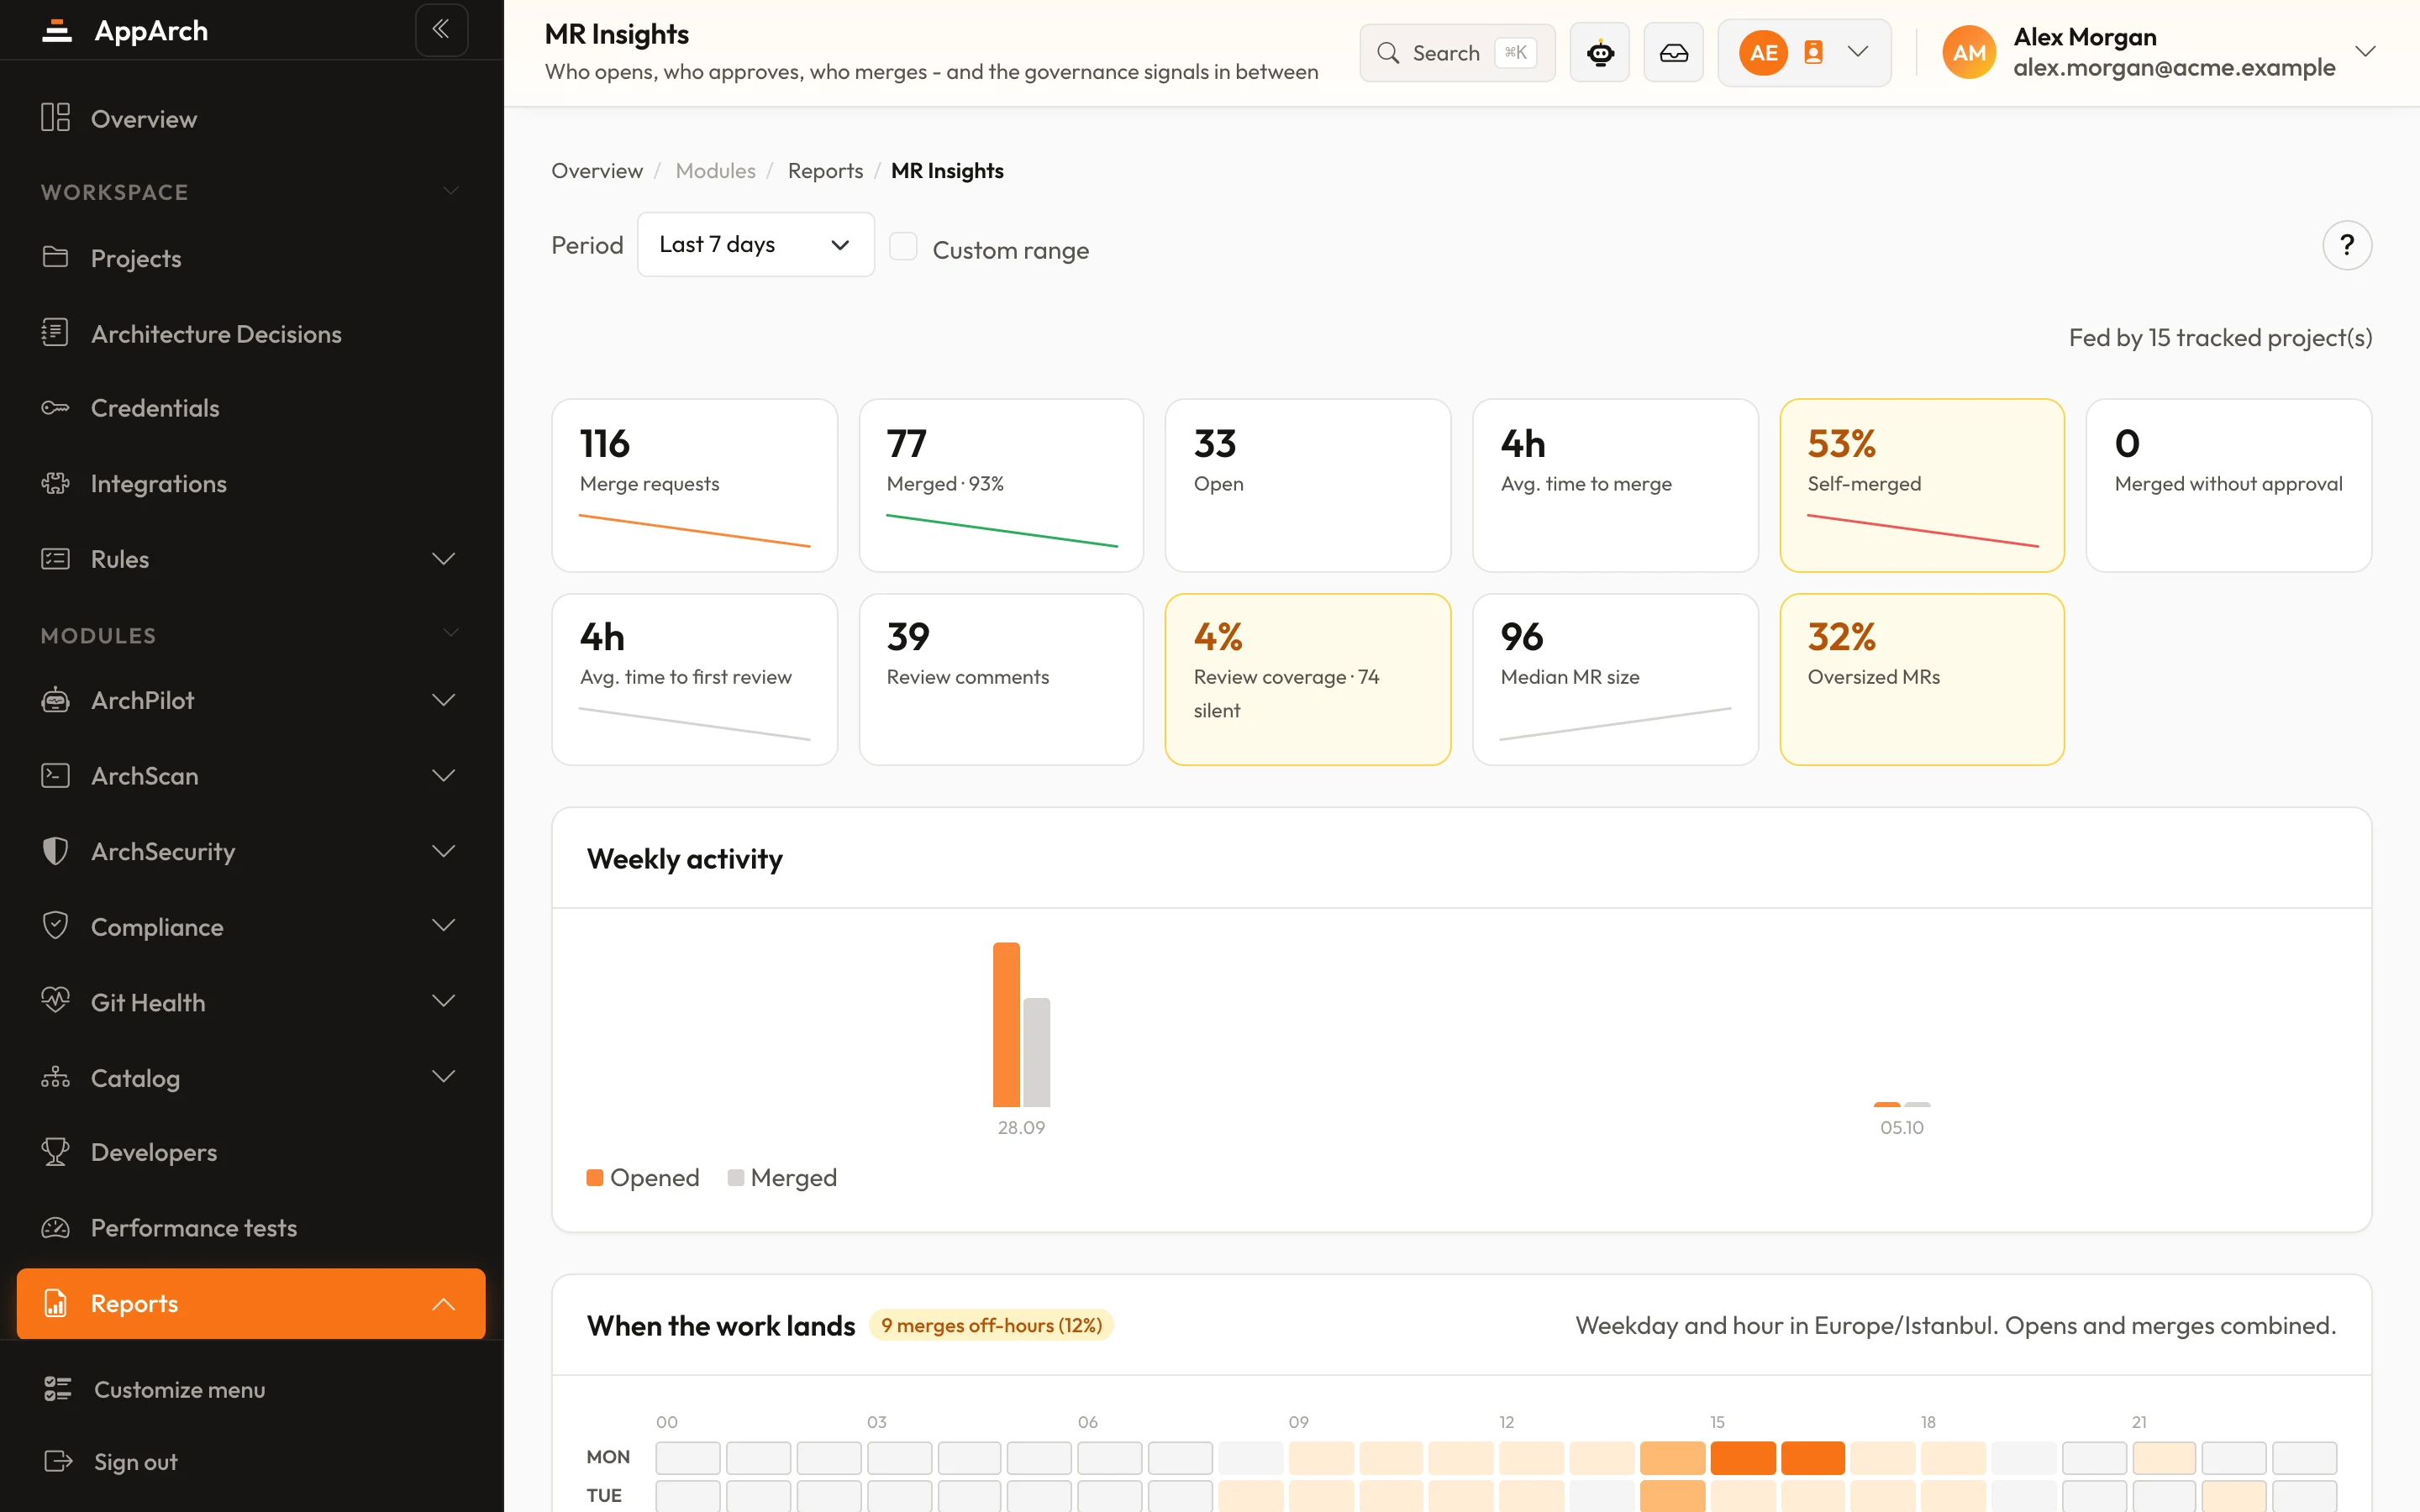
- Merge requests, approvals and review threads; MR facts every 15 minutes for MR Insights
- Branch protection and merge settings, for Git Health
- Single files and the file tree, for Compliance; nothing is cloned
- Names of Actions secrets, to check the CI setup; values cannot be read
What it writes
- Inline comments on the lines the change added
- An AppArch section in the MR description, or one summary comment if that edit fails
- Resolves its own thread once the finding is gone
- Optional auto-approve or auto-reject; it refuses to approve if new commits arrived after the review
- Starts scheduled and on-demand scans with a repository_dispatch event
What it never does
- No commit statuses or check runs: the pipeline result is your CI job's own exit code
- Never clones or uploads the repository to the panel
- Never registers webhooks itself; paste the URL if you want one
- github.com only; GitHub Enterprise Server is not supported
- Tag protection and release tracking are not read
Personal access token, fine-grained or classic. Its scopes and expiry are read from GitHub and shown in the panel; an expired token is refused before any call. Tokens are not refreshed.
When things happen
- 5 sComments are posted
- 10 sNew findings are matched to their threads
- 5 minMerge request state and approvals are re-read
- 10 minMembers are synced
- 15 minMR facts for MR Insights
A webhook makes the merge request state change immediate instead of waiting for the next poll.
See it in the product
All screenshots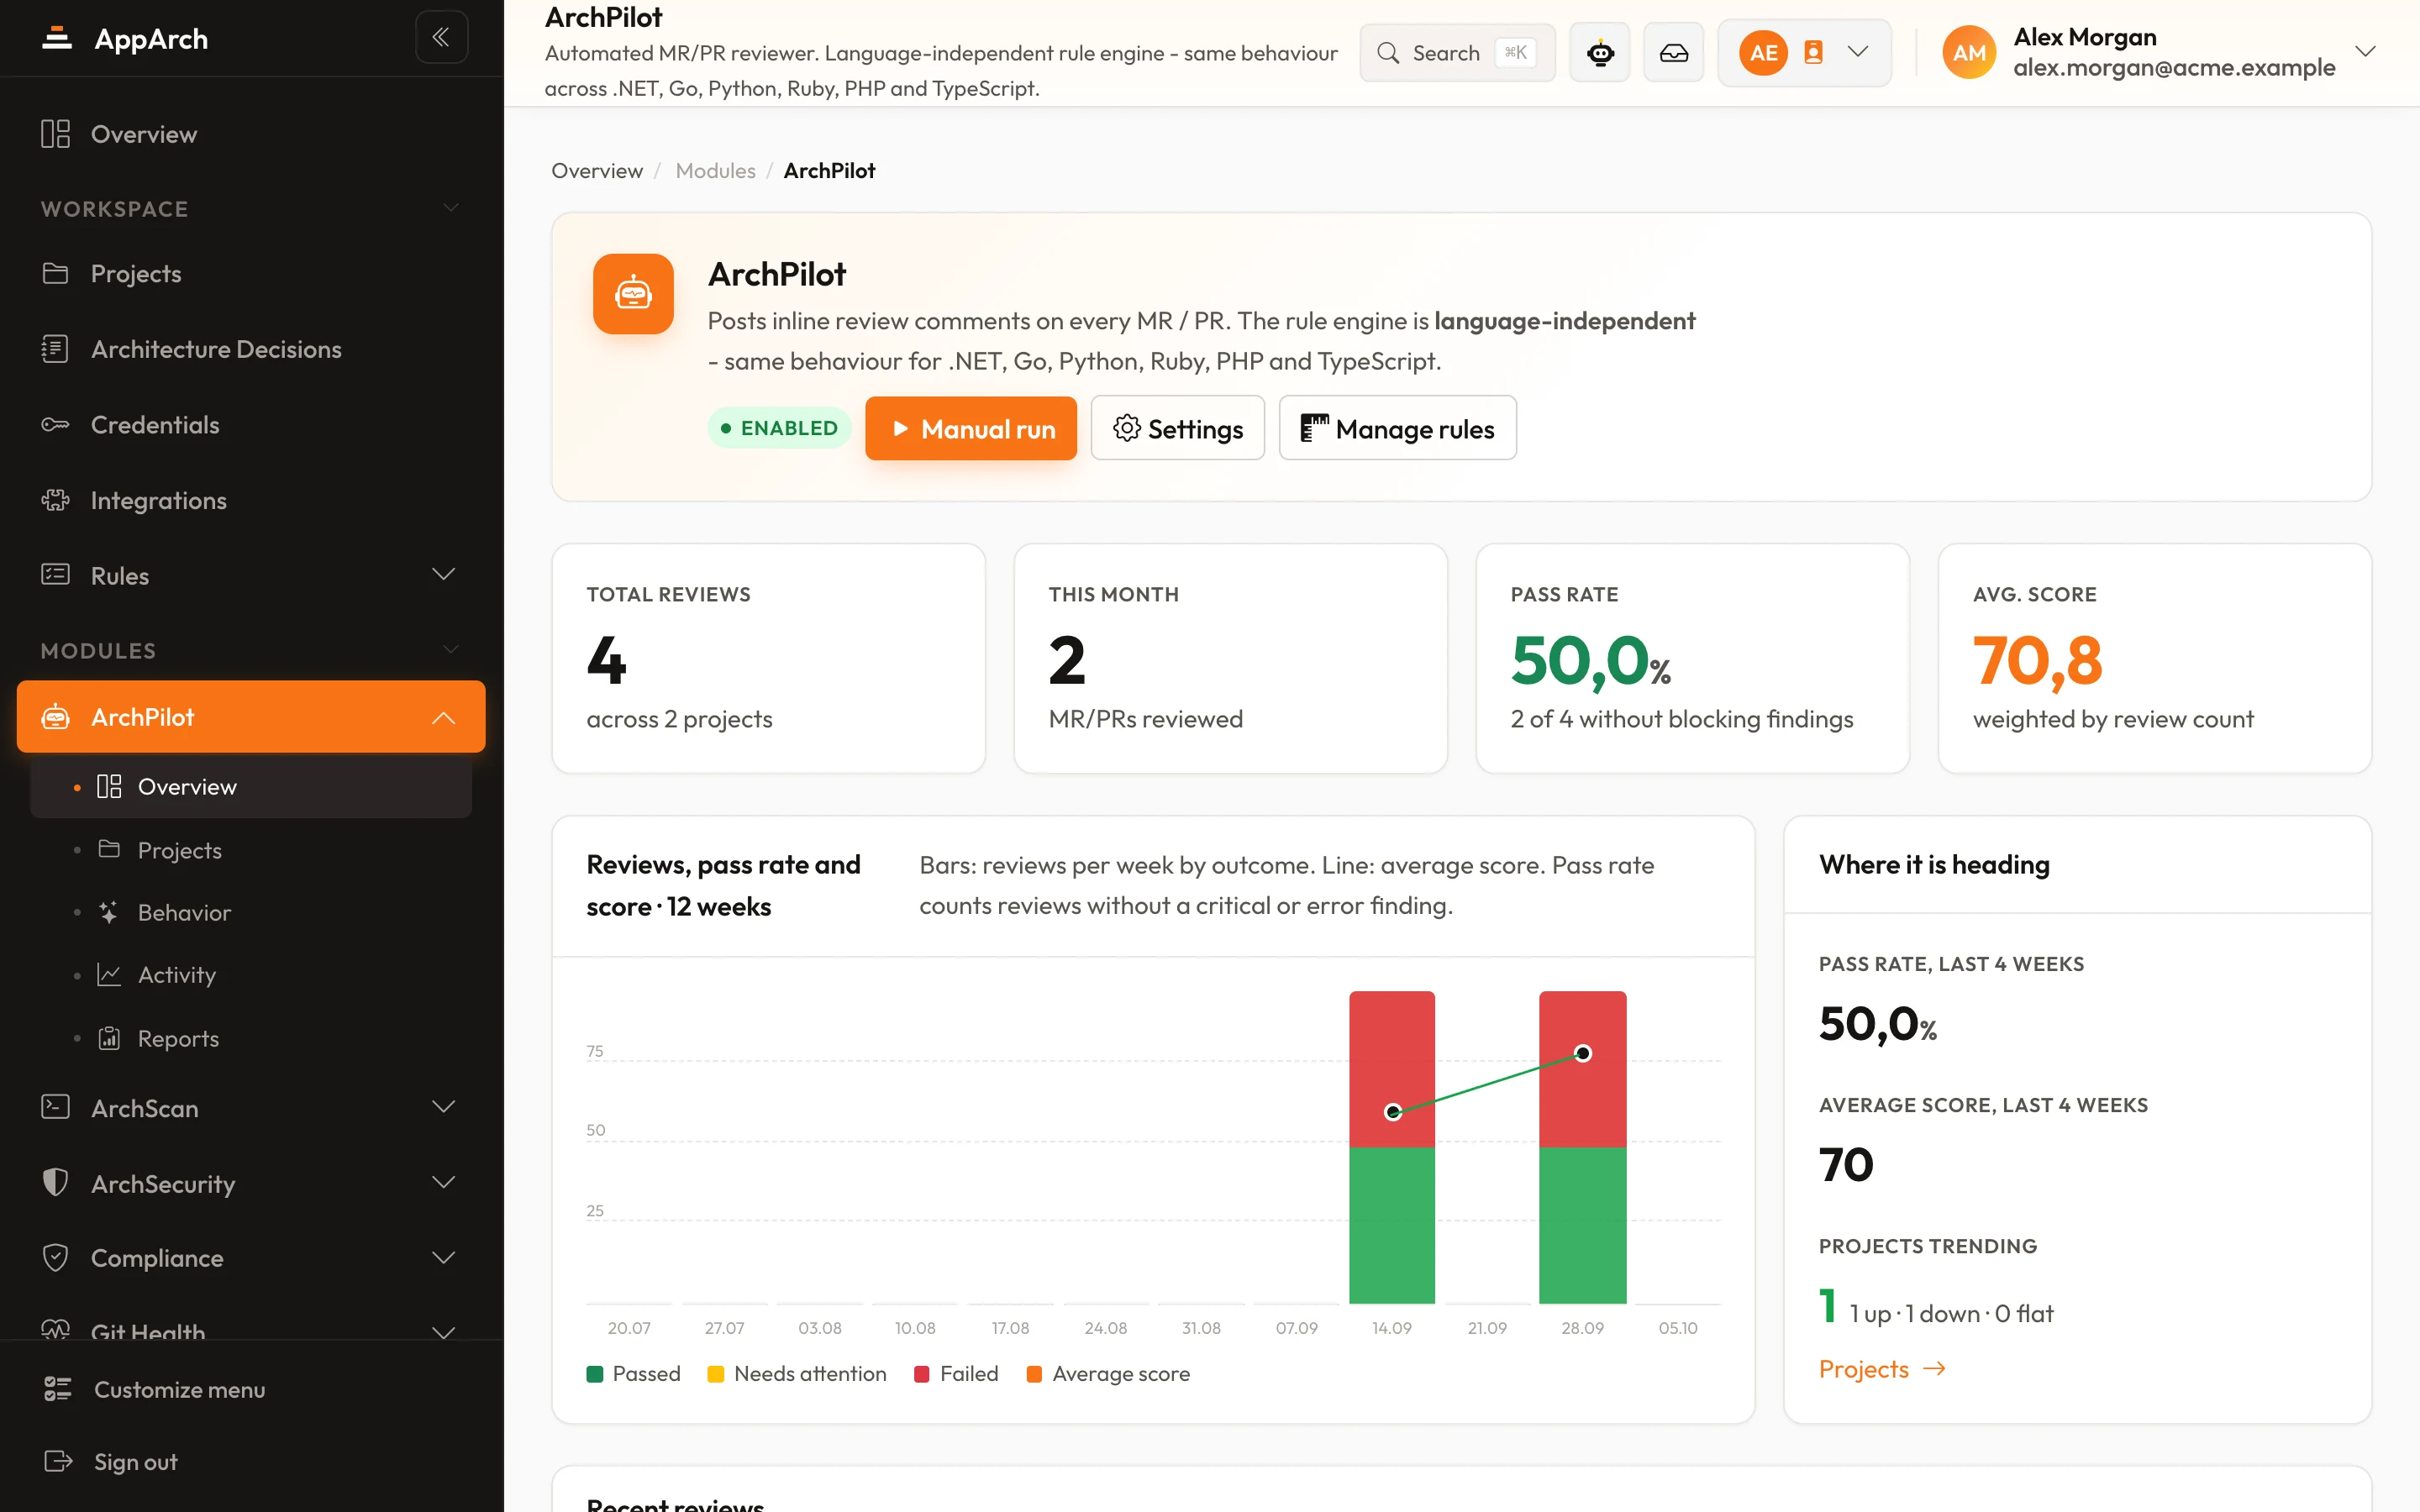
Connect GitHub
Connect in minutes - your first review lands on the next change.